Platform

Exactly who sees exactly what

Twelve permission modules, around forty-five keys, custom roles and per-person overrides — enforced on the server.

Proof Points

  • 12 modules, ~45 keys
  • Scope axes: all / assigned / own / campaigns / none
  • 4 built-in roles, unlimited custom roles, per-user overrides
  • Server-side enforcement including request clamping in the inbox
  • Live membership re-verification
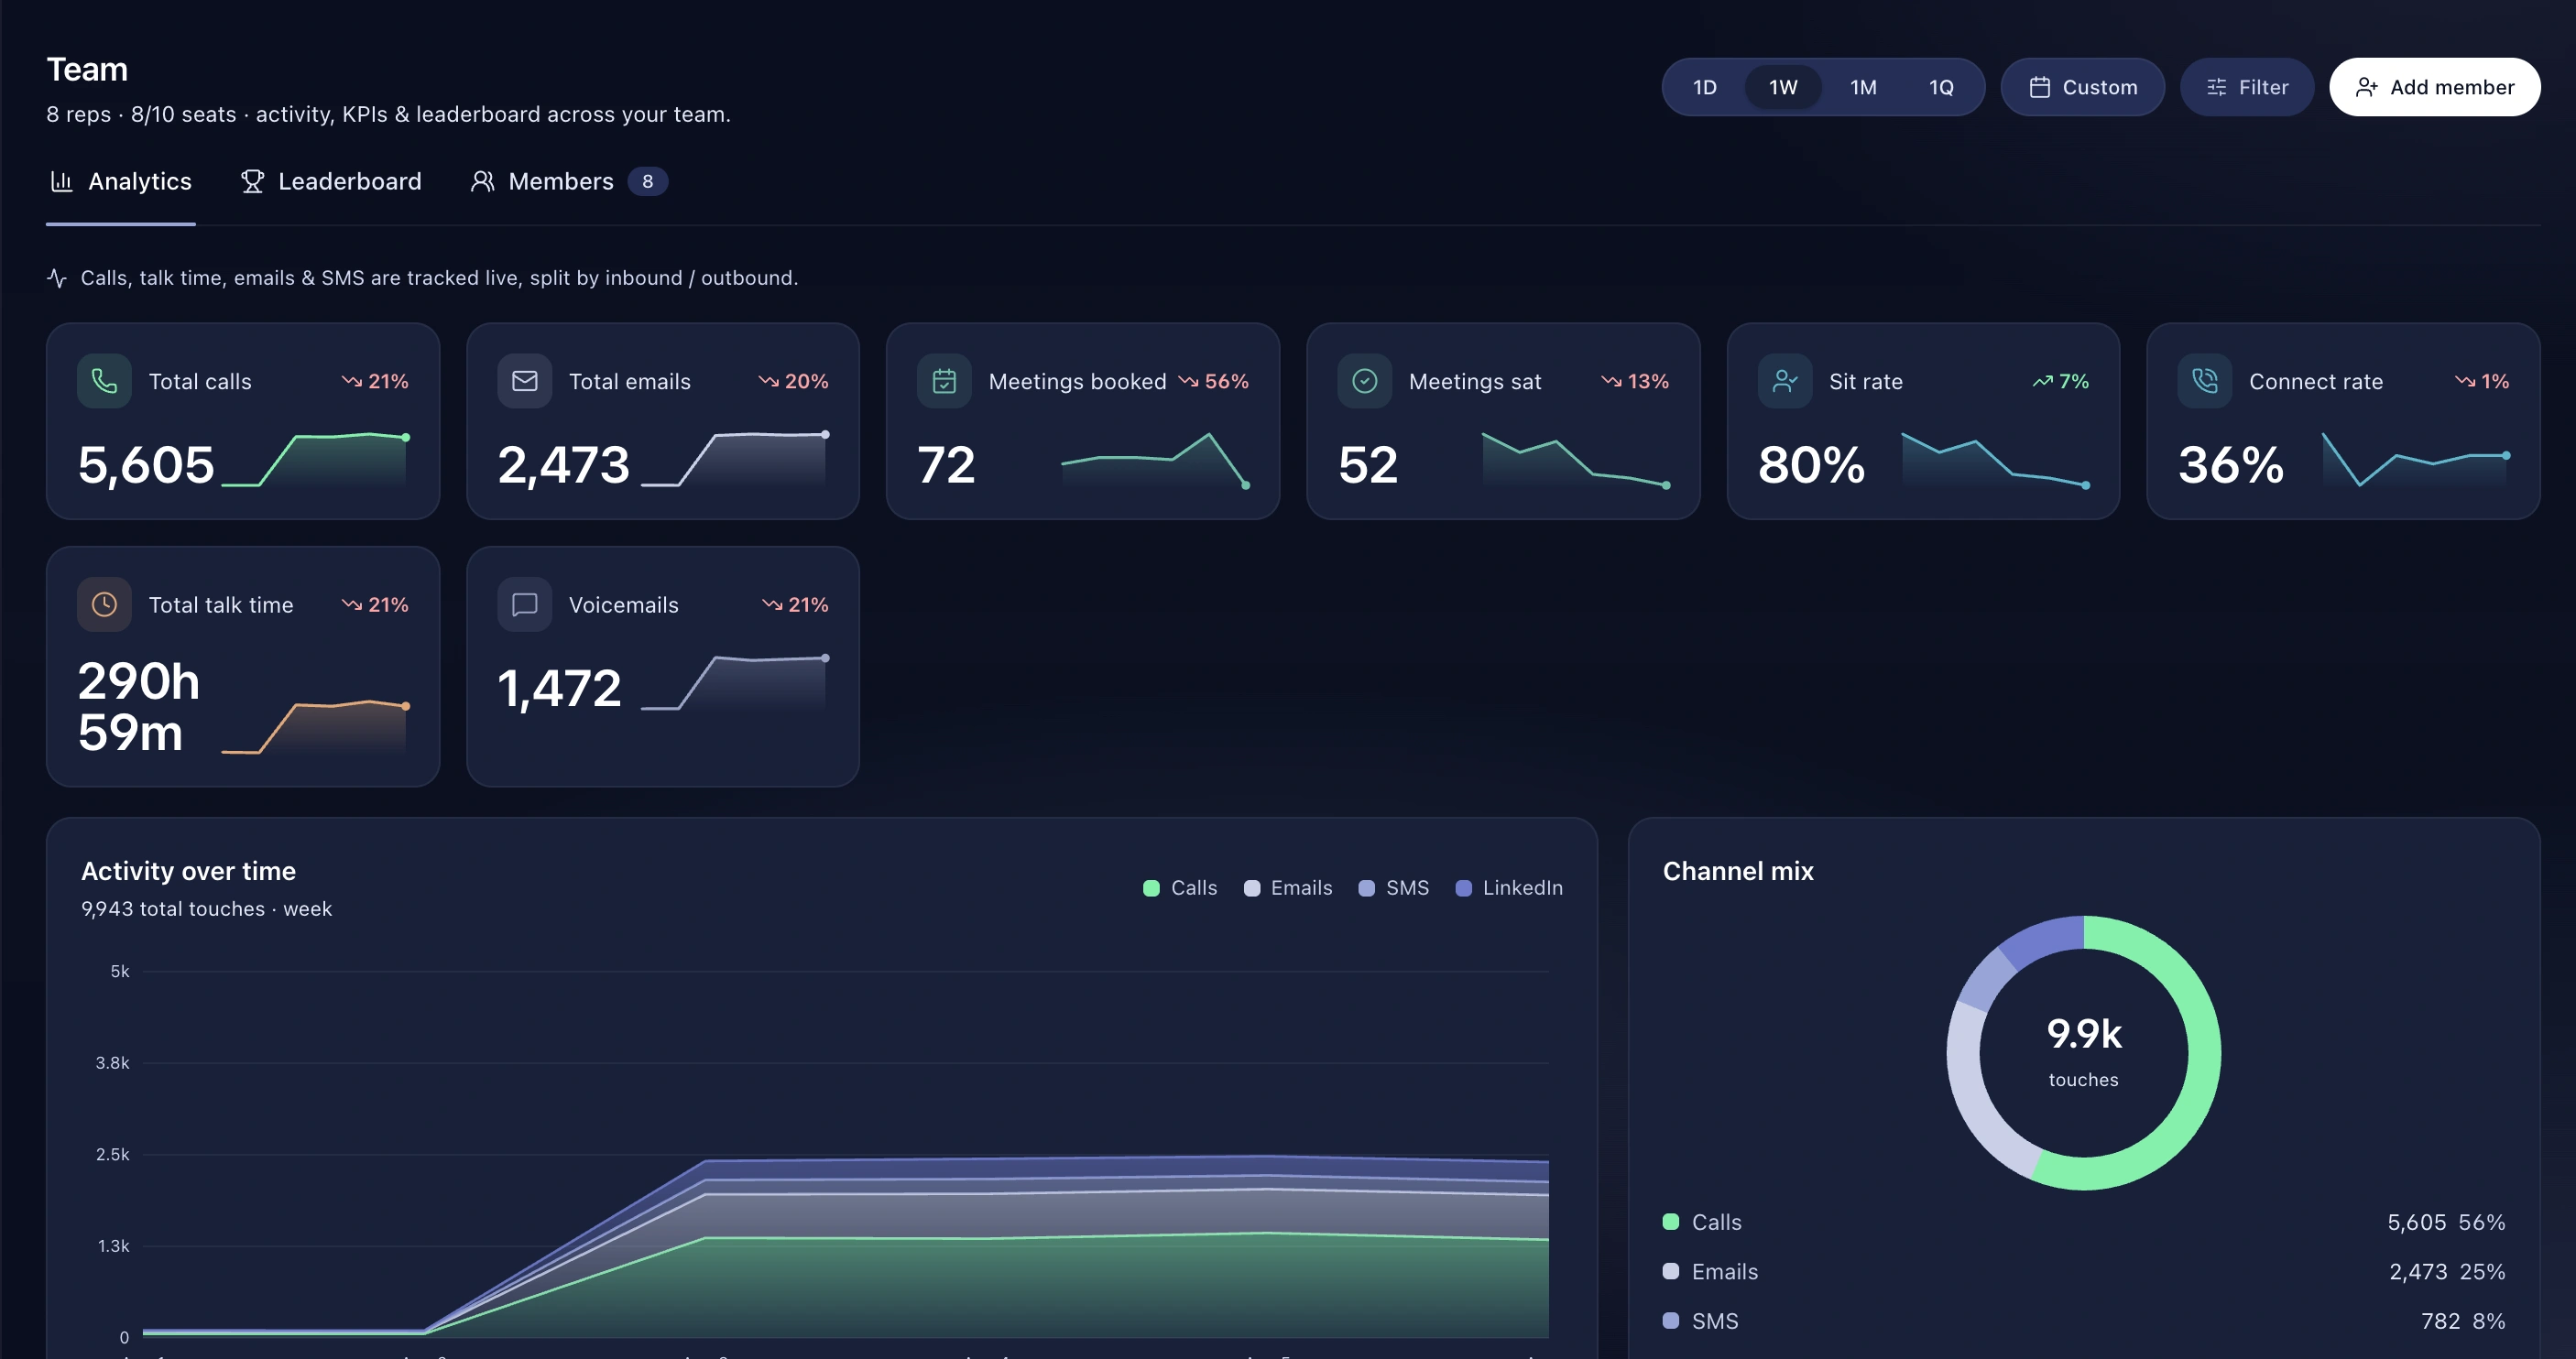
  • Departments and per-rep KPI targets
  • Everyone can connect their own mailbox and calendar so they can be booked in

How It Works

  1. Start from a built-in role
  2. Create custom roles for your structure
  3. Override individuals where needed
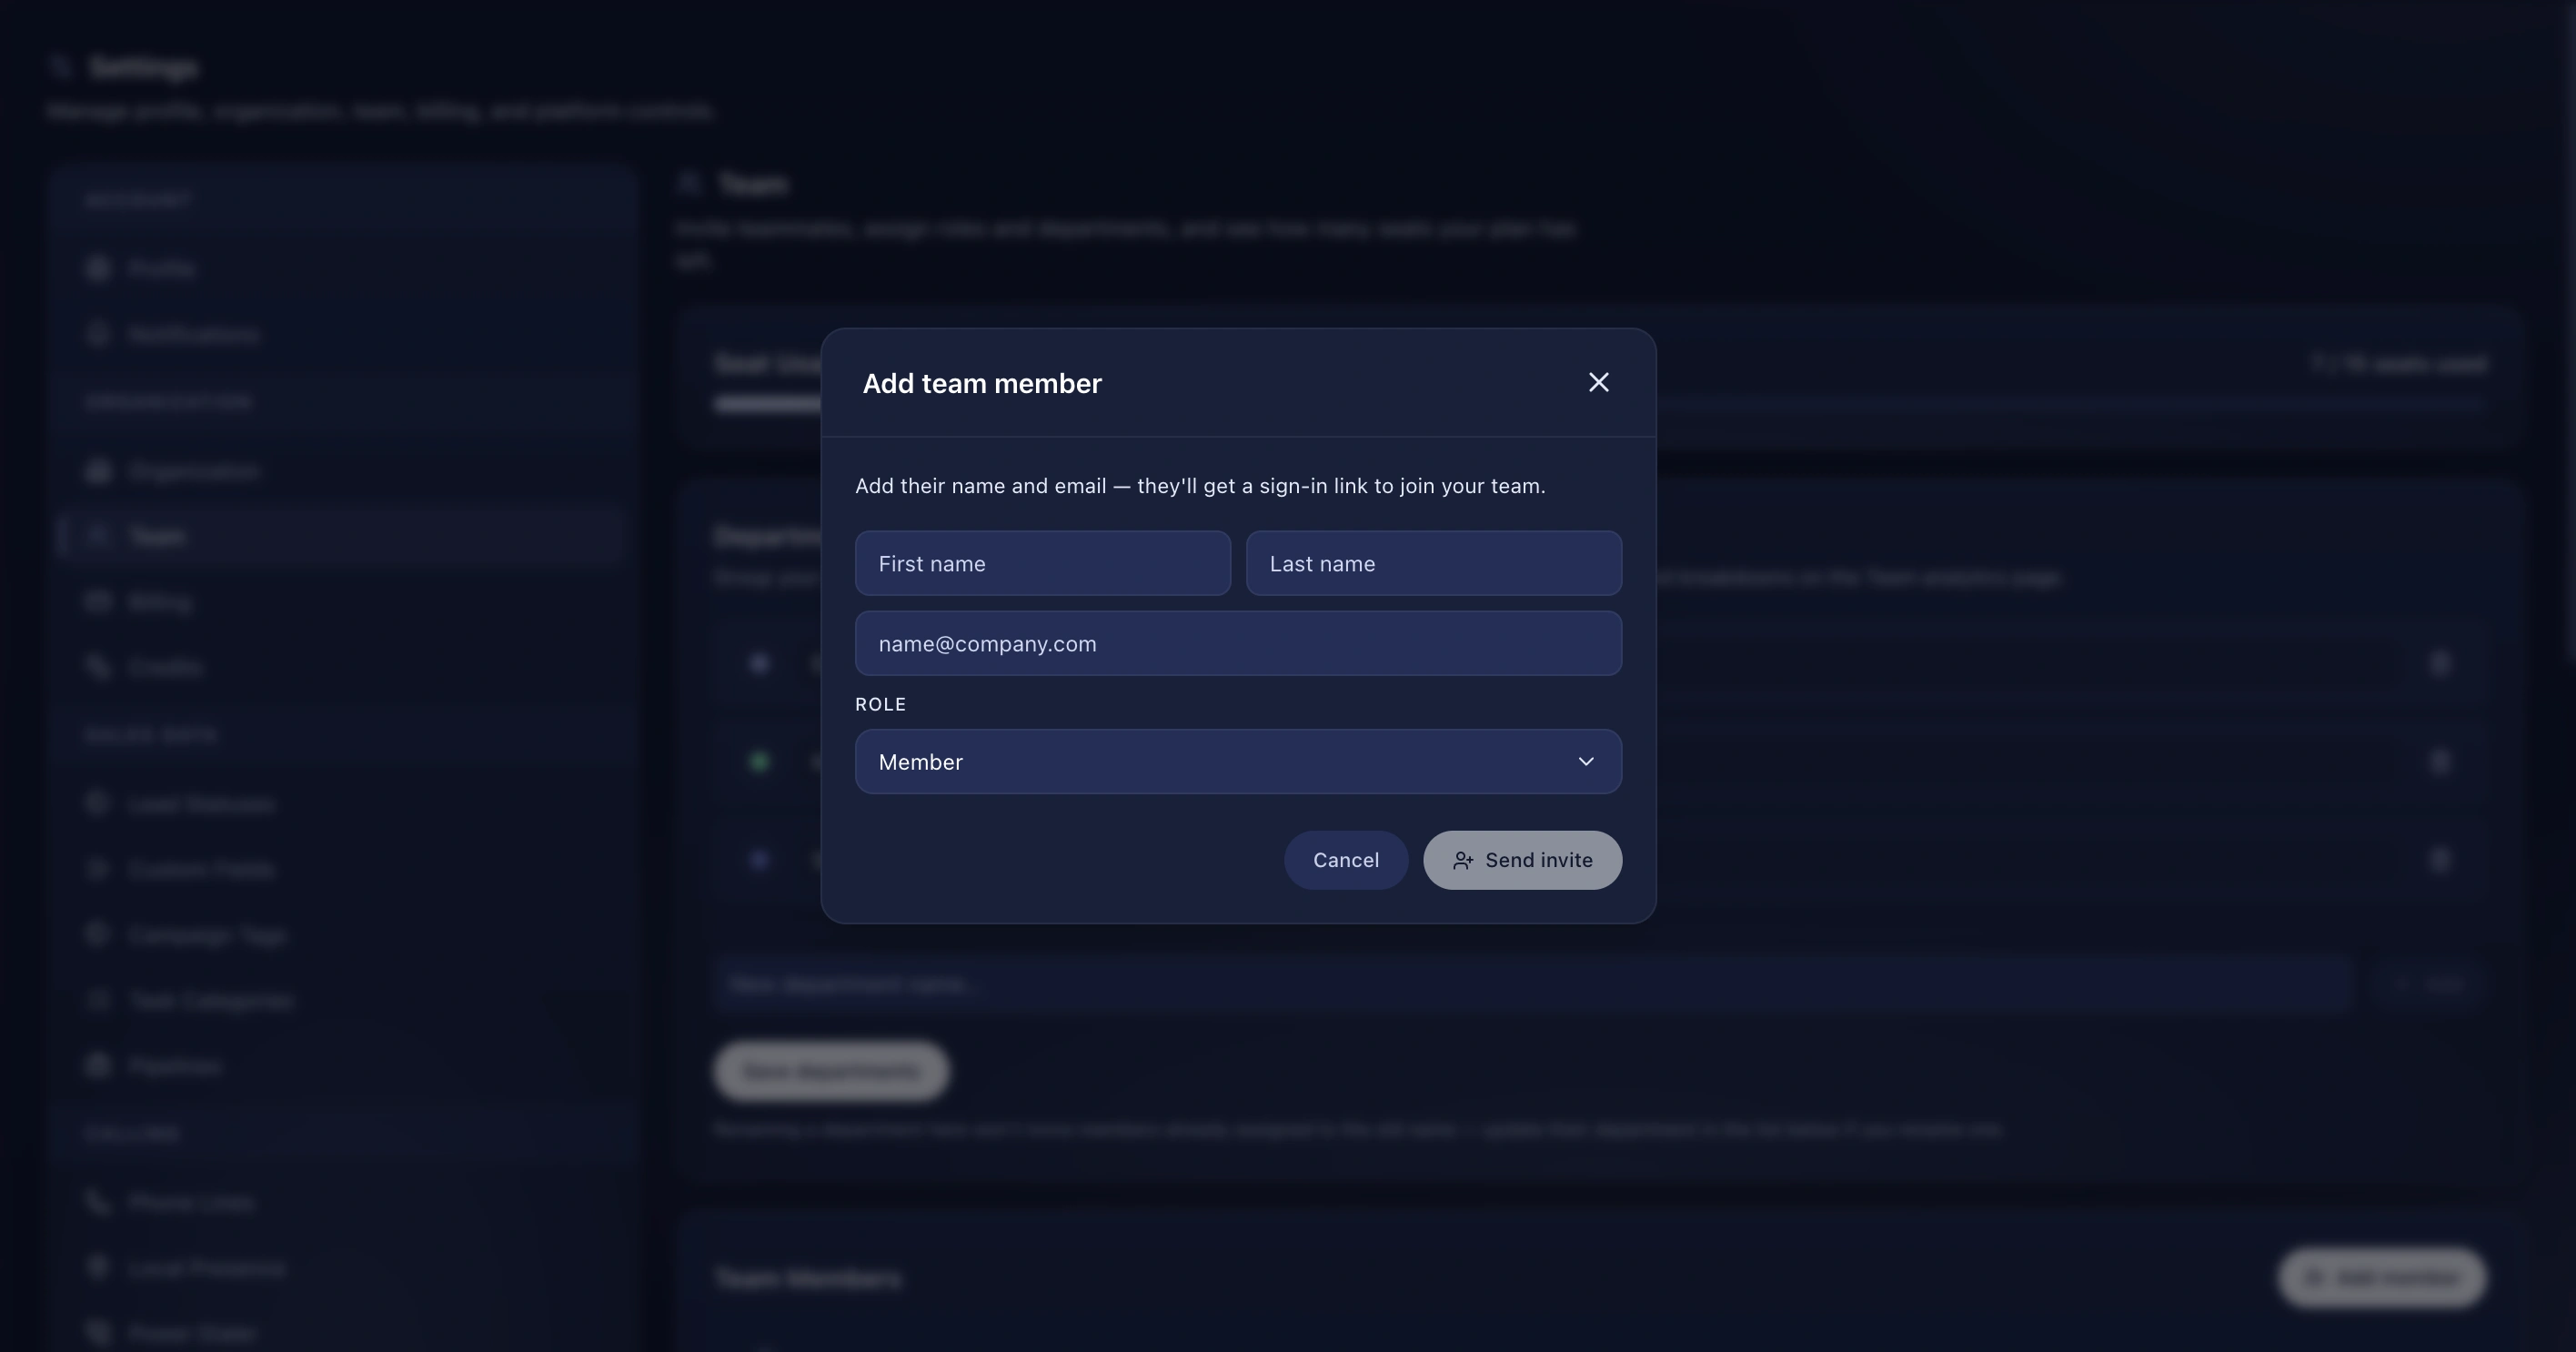
  4. Assign on invite

Benefits

Scopes, not just switches

"Can view leads" isn't one question. A rep might see all leads, only leads in campaigns they're on, or none. The same for opportunities, the inbox, recordings and analytics.

Custom roles and per-person exceptions

Four built-in roles to start from, unlimited custom roles, and sparse per-person overrides on top for the one person who needs one extra thing.

Enforced where it counts

Permissions are applied on the server. A rep whose inbox is scoped to their own conversations has the request narrowed before the query runs — hiding a button is not a permission.

Removal takes effect immediately

Every request re-verifies that the person is still a member of the organisation. Remove someone and their access ends on their next request, not whenever their session happens to expire.

Frequently asked questions

Can I stop reps exporting data?

Yes, it's its own permission.

Can a manager see only their team?

Yes, via scope.

Are custom roles on every plan?

Explore